Privacy and artificial intelligence regulation is becoming a practical business issue in 2026, not just a concern for large technology companies. A small retailer may use an email platform that tracks customers, a professional service firm may rely on cloud software that stores client information, and an online business may use an AI chatbot or automated marketing system. Each choice can create legal obligations that vary by state.
Businesses must look at where they operate, where customers live, how much personal data they handle, whether they sell or share information, and whether they use sensitive data or automated decision-making. In 2026, new state privacy laws and AI-specific rules made that patchwork more complicated.
City Law Guide provides general educational information, not legal advice. Small businesses should review the laws that apply to their locations, customers, industry, and technology before making compliance decisions.
Why 2026 Is a Turning Point for Privacy and AI Compliance
Indiana and Kentucky comprehensive consumer privacy laws took effect on January 1, 2026, and Rhode Island also joined the growing group of states with comprehensive privacy requirements in 2026. California’s updated privacy regulations became effective January 1, 2026, adding detailed requirements in areas such as privacy risk assessments, cybersecurity audits, and automated decision-making technology, although some compliance dates are phased in.
The result is a business environment in which a company can be too small to trigger one state’s comprehensive privacy statute but still have obligations under another law, a contract with a larger customer, a sector-specific rule, a breach-notification statute, or a rule governing sensitive data.
New State Privacy Laws Are Expanding the Patchwork
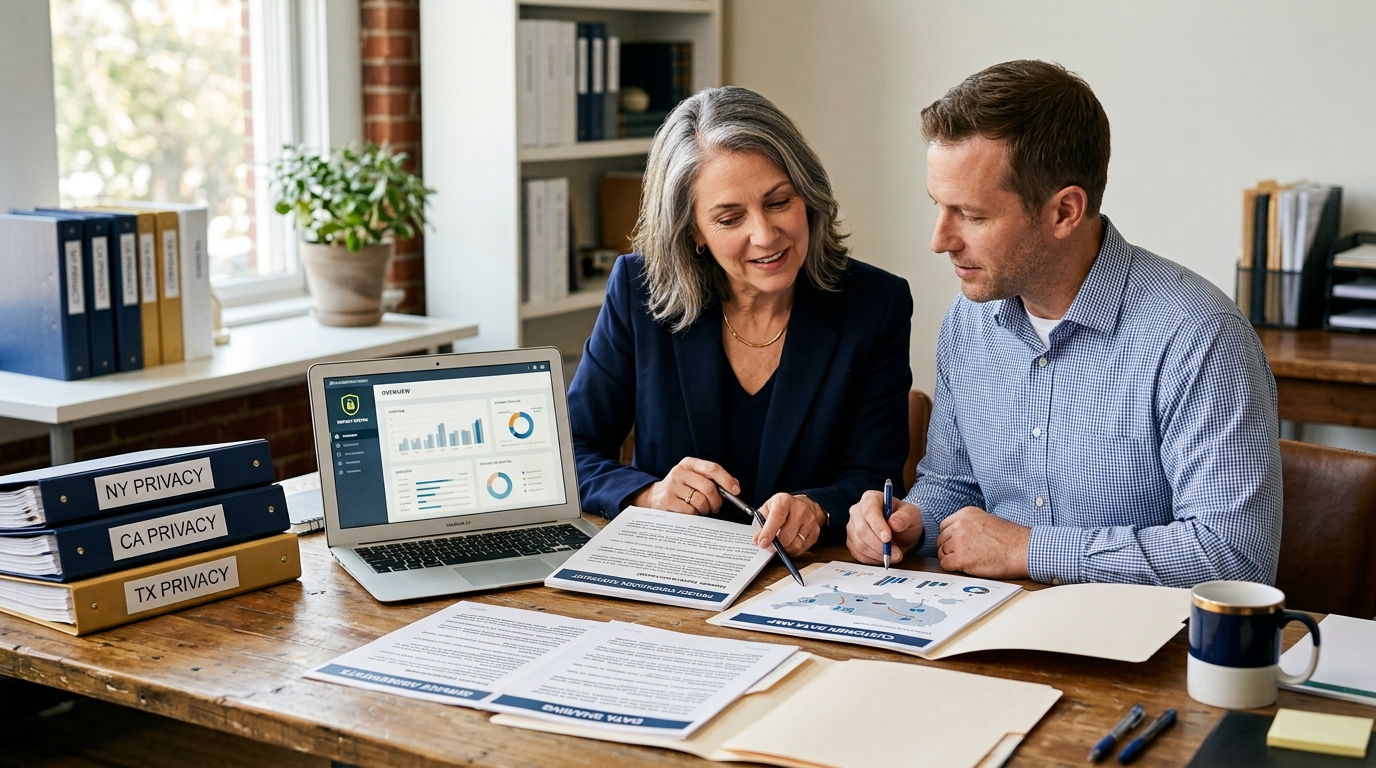
Indiana’s Consumer Data Protection Act generally applies to businesses that operate in Indiana or target Indiana residents and meet certain data-volume or data-sale thresholds. Kentucky uses a similar threshold structure. Both laws give covered consumers rights such as access, correction, deletion, portability, and the ability to opt out of certain uses of personal data.
Many small businesses may fall outside these comprehensive statutes. However, a company that grows quickly, operates across state lines, or relies heavily on data-driven advertising can cross a threshold faster than expected. A business may also face privacy and security duties through contracts with larger customers.
Readers can also visit the Business Law category or the Legal Topics hub.
Small Business Exemptions Are Not Universal
One of the biggest mistakes a small business can make is assuming that “small business” has the same meaning everywhere. Privacy statutes use different coverage tests. Some focus on the number of residents whose data is processed. Others look at revenue from selling personal data, whether the company sells sensitive information, or whether the organization belongs to a regulated industry.
Texas provides a useful example. Its Data Privacy and Security Act generally exempts small businesses as defined by the federal Small Business Administration, but a small business that sells sensitive personal data must obtain consumer consent before doing so. An exemption from most of a statute does not always mean exemption from every requirement.
A business should create a simple coverage map showing where customers are located, what categories of data are collected, which vendors receive that data, and whether the business sells, shares, profiles, or uses data for targeted advertising.
Sensitive Data Deserves Extra Attention
Sensitive data can include precise geolocation, biometric identifiers, health information, children’s data, religious beliefs, racial or ethnic origin, sexual orientation, immigration or citizenship status, and other categories defined by state law. The exact definition differs by jurisdiction, but the compliance risk is usually higher than for ordinary contact information.
Small businesses should avoid collecting sensitive data merely because a software platform makes it easy. A fitness studio may not need to retain detailed health information indefinitely. A local app may not need continuous precise location access. A website may not need to store dates of birth if age verification can be handled another way.
Data minimization reduces both legal exposure and security risk. Businesses should also know how long sensitive data is retained, who can access it, and whether vendors can use it for their own purposes.
AI Rules Are Moving Beyond General Privacy Notices
AI systems can use personal data to generate recommendations, scores, predictions, summaries, or decisions. A business may use AI for customer service, advertising, fraud detection, employee recruiting, scheduling, pricing, or other operational tasks. Even when the business did not build the model, deploying the tool can create responsibilities.
The legal question is increasingly not just “Do we use AI?” but “What does the AI do, what data does it use, and does it affect a person’s rights or opportunities?” A writing assistant is different from a system that materially influences employment, lending, insurance, housing, education, or health-related decisions.
Small companies should maintain an inventory of AI tools. That list should identify the provider, purpose, data inputs, outputs, retention practices, human review, and whether the tool affects consumers, employees, or applicants.
California Adds Risk Assessments and ADMT Rules
California’s finalized CCPA regulations took effect January 1, 2026. Among other areas, they address privacy risk assessments, cybersecurity audits, and automated decision-making technology. Covered businesses subject to risk-assessment requirements began compliance in 2026, while certain automated decision-making technology requirements are scheduled to begin January 1, 2027. Cybersecurity-audit certification deadlines are phased in later based on business size.
For small businesses, the key lesson is that privacy compliance is becoming more operational. A privacy policy alone may not be enough. Businesses may need documented assessments, governance processes, records showing why a data practice is necessary, and procedures for responding to consumer rights.
Companies serving California customers should determine whether the CCPA applies to them rather than assuming it does or does not based only on employee count. Review the California Privacy Protection Agency’s official privacy regulations for authoritative information about the current requirements.
Texas and Colorado Show Different AI Approaches
Texas’s Responsible Artificial Intelligence Governance Act became effective January 1, 2026. The law restricts certain harmful or discriminatory uses of AI and gives the Texas Attorney General enforcement authority. It shows that states are beginning to regulate AI directly rather than treating every AI issue solely as a privacy matter.
Colorado’s approach is evolving as well. Legislation enacted in 2026 replaced earlier high-risk AI provisions with a new automated decision-making framework scheduled to take effect January 1, 2027. The Colorado Attorney General is conducting rulemaking ahead of that date.
For a small business operating nationally, AI compliance cannot be based on one state’s checklist. Requirements may vary depending on where a tool is deployed and what decision it influences.
What Small Businesses Should Do Now
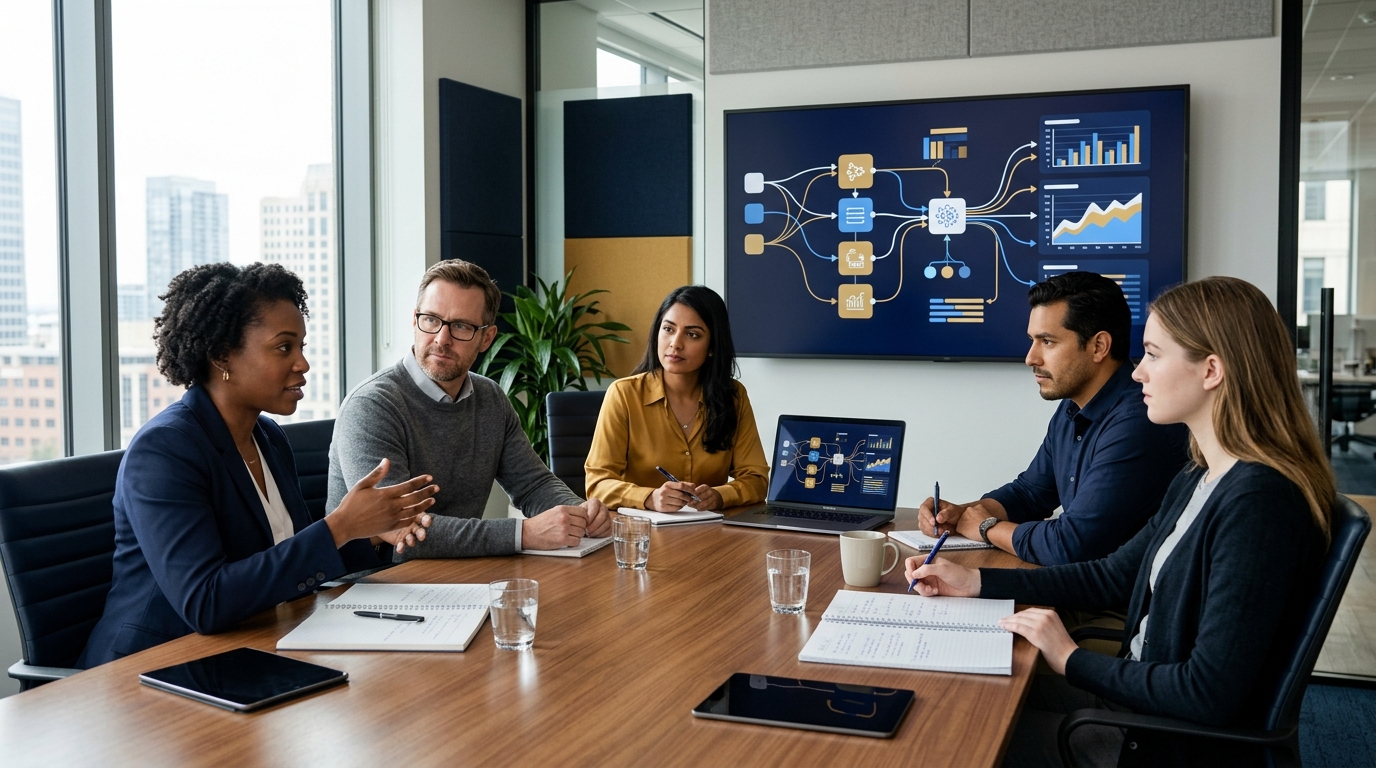
The goal is not to turn every small company into a privacy law department. The practical goal is to understand the business’s data and AI uses well enough to identify high-risk areas before they create a complaint, contract problem, regulatory inquiry, or data breach.
Privacy compliance works best when connected to ordinary operations rather than treated as a document updated once a year and forgotten.
Build a Practical 2026 Compliance Checklist
Start by listing the personal information your business collects through its website, ecommerce platform, forms, email marketing, customer relationship software, analytics, payment systems, employee tools, and apps. Identify where that information is stored and which third parties can access it.
Next, review your public privacy notice. It should accurately describe current practices rather than copying generic language from another website. Make sure consumer request methods work and that staff know who is responsible for responding. Review cookie, targeted advertising, data-sale, and opt-out practices in the states where they matter.
Then audit AI use. Ask employees which AI tools they use, including free browser-based tools that may never have gone through formal approval. Determine whether confidential, customer, employee, or sensitive information is being entered into those systems. Establish rules for what can and cannot be submitted.
Vendor contracts
Vendor contracts deserve attention too. Cloud platforms, marketing providers, AI vendors, payroll systems, and analytics tools may process personal data on your behalf. Check terms for data use, security, breach notification, deletion, subprocessors, and whether the vendor can train AI models using your business data.
Finally, create a basic incident-response plan. Know who will investigate a suspected breach, preserve records, contact vendors, assess notification requirements, and communicate with affected individuals if necessary.
Businesses can continue with City Law Guide’s Legal Resources section for practical information, explore City Legal Guides for location-specific context, or use the Directory when local professional guidance is appropriate. Companies hiring workers with automated tools may also want to read AI Hiring and Pay Transparency in 2026: What Job Seekers Need to Know.
The strongest 2026 strategy is simple: collect less data, know where the data goes, document important decisions, review AI tools before they affect people, and revisit state coverage as the business grows. Privacy and AI law will continue to change, but a company with a clear data inventory and responsible governance process will be better positioned to adapt.